
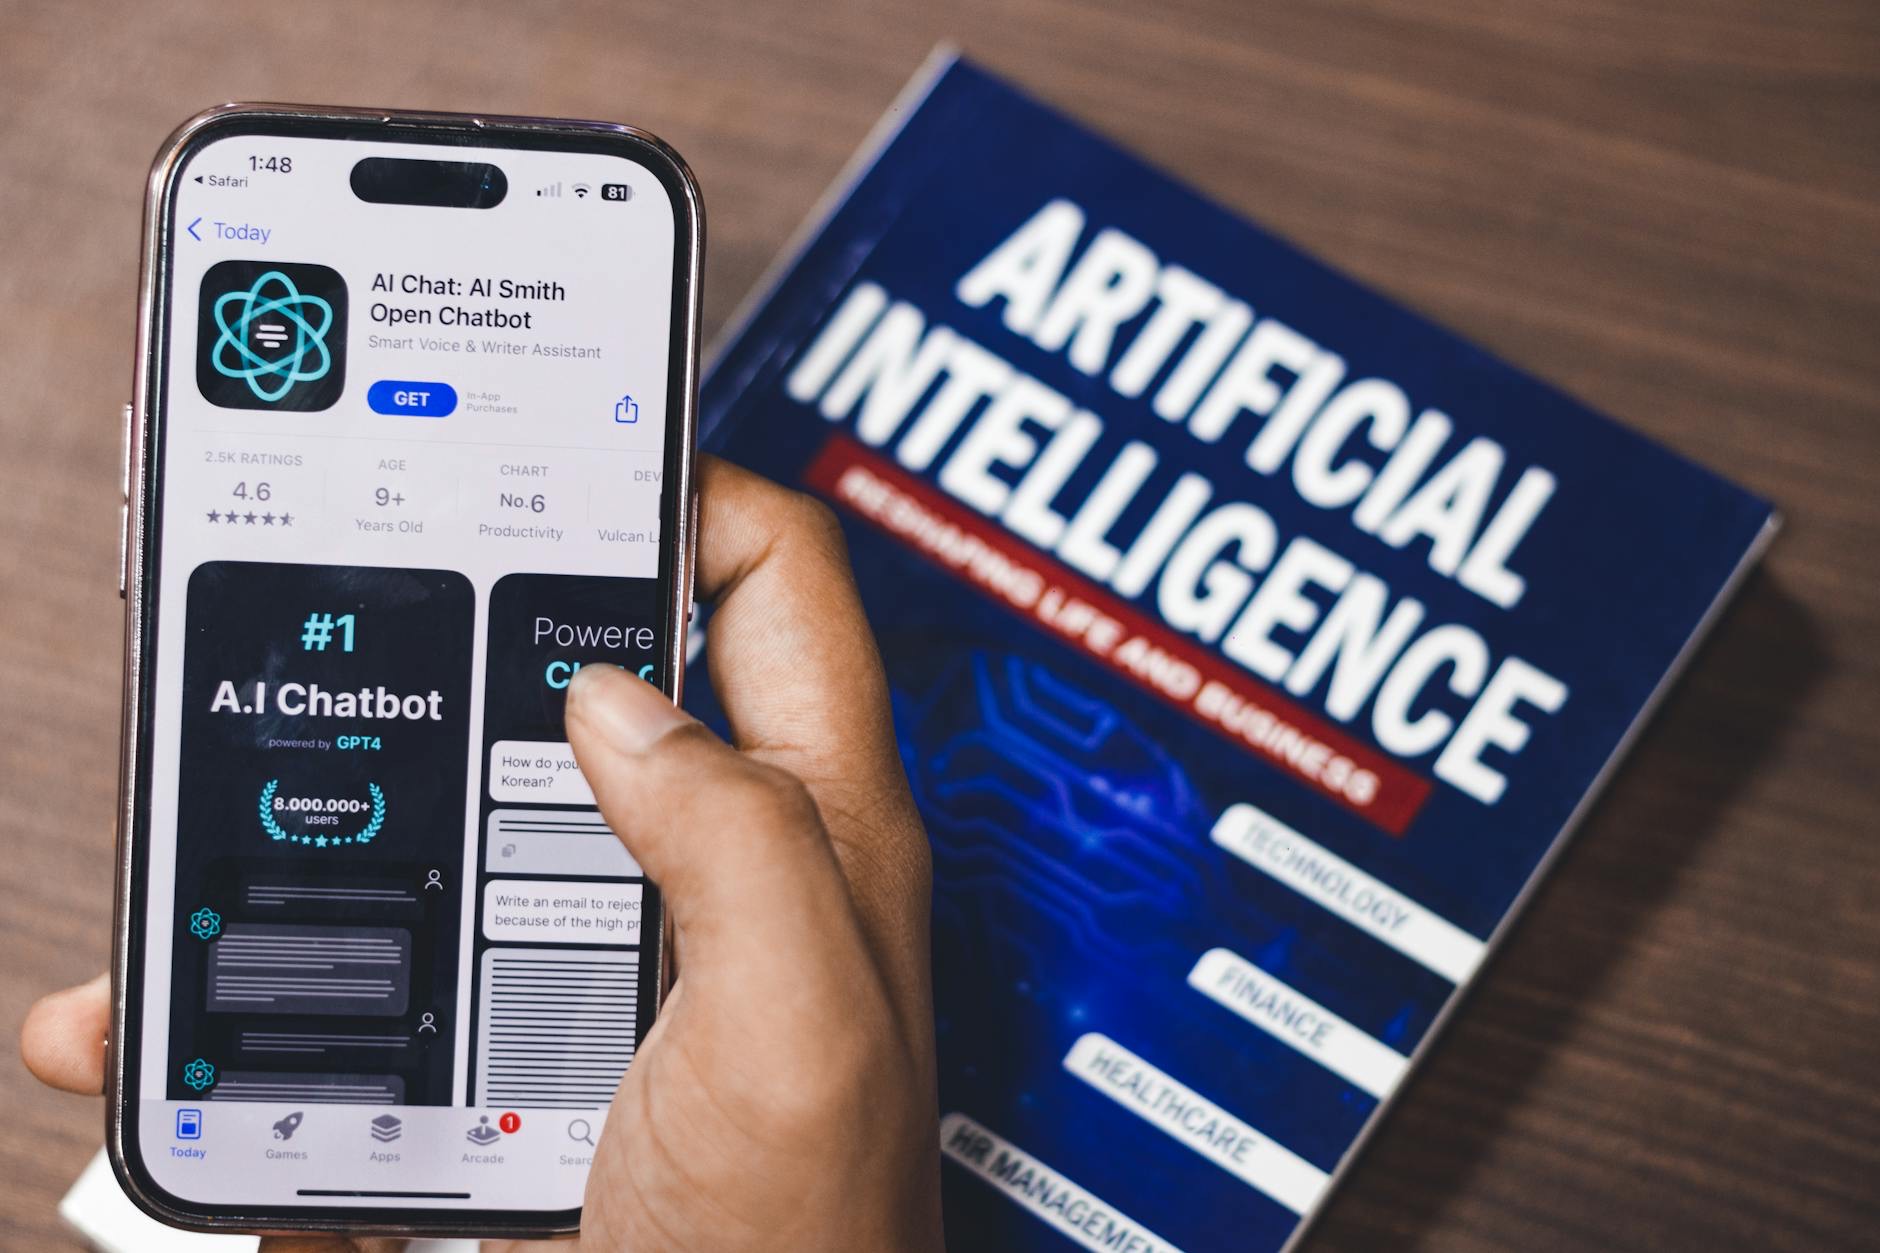
Security concerns surrounding advanced artificial intelligence systems moved sharply higher on the agenda across Silicon Valley and Washington this week as executives, researchers, and policymakers intensified warnings about the pace of AI deployment and the potential consequences of inadequate safeguards.
The conversation gained momentum after multiple public discussions and research commentaries compared the current phase of AI development to the run-up to the Year 2000 computer transition, often referred to as Y2K. During that period, governments and corporations invested heavily in identifying and mitigating software vulnerabilities tied to date formatting systems that many feared could disrupt financial networks, transportation infrastructure, utilities, and government systems.
Industry analysts say the comparison reflects growing concern that frontier AI systems are becoming integrated into critical workflows before consistent security standards are fully established. Unlike the Y2K issue, however, today’s risks are viewed as more open-ended, involving autonomous behavior, cyber operations, synthetic media, and software generation capabilities that continue evolving rapidly.
In recent months, AI developers including OpenAI and Anthropic have expanded safety testing programs tied to advanced models. The companies have publicly discussed risks related to cyber misuse, biological knowledge assistance, deceptive outputs, and model autonomy. Anthropic in particular has increasingly positioned constitutional AI and scalable oversight as core parts of its development framework.
Federal agencies and lawmakers have also intensified scrutiny of frontier AI systems. U.S. regulators have continued evaluating export controls on advanced semiconductors and AI infrastructure, while national security officials have raised concerns about the potential misuse of generative AI tools in cyberattacks, influence operations, and critical infrastructure targeting.
The Biden and Trump administrations both elevated AI as a strategic technology priority over the past several years, although policy approaches differed on regulation and industry coordination. By 2026, many large enterprise customers are no longer treating AI governance as a future planning issue but as an operational procurement requirement.
Major cloud providers and enterprise software companies are now investing heavily in AI security layers designed to monitor prompts, detect abnormal outputs, restrict model access, and identify attempts to exploit vulnerabilities. Security startups focused on model auditing, AI observability, and synthetic content detection have also seen increased investor interest.
The latest debate comes as generative AI systems are becoming more deeply integrated into software engineering and automation workflows. Some researchers have warned that increasingly capable coding systems may eventually identify exploitable vulnerabilities or assist attackers in scaling cyber operations more efficiently.

At the same time, industry leaders have cautioned against overstating near-term catastrophic scenarios. Many researchers argue that today’s practical risks are more immediate and measurable, including phishing campaigns, fraud automation, misinformation generation, insecure enterprise deployments, and data leakage through improperly configured AI systems.
Cybersecurity firms have reported rising use of generative AI in social engineering attacks and impersonation campaigns targeting corporations and consumers. Security analysts say the accessibility of large language models has lowered barriers for creating convincing fraudulent communications, multilingual scams, and automated reconnaissance tools.
Within Silicon Valley, the debate has increasingly shifted from whether regulation will arrive to what form it should take. Some AI firms have advocated for evaluation-based oversight systems focused specifically on frontier models exceeding defined capability thresholds. Others have warned that excessive regulation could entrench dominant players by making compliance prohibitively expensive for startups.
Open-source AI development has become another major point of disagreement. Supporters argue open models accelerate innovation, transparency, and independent research. Critics counter that unrestricted distribution of highly capable systems may create security challenges that are difficult to contain once models become widely accessible.
Investors are also watching the debate closely because AI infrastructure spending remains one of the strongest drivers of technology capital expenditures. Semiconductor firms, hyperscale cloud providers, and data center operators continue expanding aggressively to support AI workloads. Any major regulatory shift affecting deployment timelines or liability exposure could influence spending patterns across the sector.
Anthropic and OpenAI have both expanded engagement with government agencies and external evaluators as pressure grows for more formalized safety reporting. Industry groups and research organizations have meanwhile called for broader adoption of standardized benchmarks for evaluating model capabilities and misuse risks.
Some policy experts believe the “Y2K moment” framing reflects an attempt to encourage coordinated preparation before a major incident forces abrupt regulatory intervention. During the original Y2K transition, companies and governments spent years auditing systems, conducting simulations, and coordinating remediation efforts. Advocates of stronger AI governance argue a similarly proactive approach is needed now.
Others caution that the comparison has limits. Y2K involved a relatively specific technical flaw with a fixed deadline, while AI systems evolve continuously and present a moving target for regulators and developers. Critics of alarmist framing also argue that exaggerated rhetoric could distort public understanding or accelerate reactionary policymaking.

Still, the broader consensus across much of the U.S. technology industry appears to be shifting toward the view that AI security can no longer be treated as a secondary concern. Enterprise buyers increasingly demand contractual assurances around data handling, model reliability, and operational controls before integrating generative AI tools into sensitive workflows.
Universities and nonprofit research institutions are also expanding AI safety initiatives. Academic researchers continue studying adversarial testing, interpretability, model alignment, and techniques designed to reduce harmful or deceptive outputs. Several institutions have called for stronger collaboration between industry and academia to improve independent evaluation standards.
In Washington, lawmakers from both parties have continued pressing technology executives on issues ranging from election integrity to national security and labor disruption tied to AI deployment. Congressional discussions have increasingly focused on whether existing agencies possess sufficient authority and technical expertise to oversee frontier AI systems effectively.
International coordination remains another unresolved issue. The United States, European Union, United Kingdom, and several Asian governments are pursuing overlapping but not identical regulatory approaches. Technology firms operating globally may eventually face fragmented compliance regimes governing model training, data usage, security testing, and deployment disclosures.
Despite disagreements over regulation and long-term risk projections, executives across much of the sector increasingly acknowledge that security governance is becoming central to the future of AI commercialization. For many companies, demonstrating trustworthy deployment practices may soon become as important as releasing more powerful models.
The broader technology market continues treating artificial intelligence as one of the industry’s primary growth engines. But as frontier systems become more capable and more widely integrated into critical infrastructure and enterprise operations, security considerations are moving from research discussions into boardrooms, procurement negotiations, and federal policy debates.
For Silicon Valley firms racing to deploy increasingly advanced AI systems, the coming months may determine whether the industry can establish widely accepted safeguards voluntarily or whether regulators eventually impose stricter frameworks after a major security failure or misuse incident.
Leave a Reply